Active Attack: Leaked ConnectWise Credentials Breach 173 Microsoft 365 Tenants
An active cybersecurity attack leverages leaked ConnectWise credentials to gain unauthorized access to 173 Microsoft 365 tenants via MSP supply-chain abuse, per GreavesNet security news. The incident highlights risks for organizations relying on managed service providers for core IT functions. For AI content creators, the breach underscores the need for secure, consolidated production platforms to reduce attack vectors.
Table of contents
An active cybersecurity attack exploiting leaked ConnectWise credentials has compromised 173 Microsoft 365 tenants, marking a significant supply-chain risk for managed service provider (MSP) clients worldwide.
What We Know About the Active ConnectWise Credential Attack
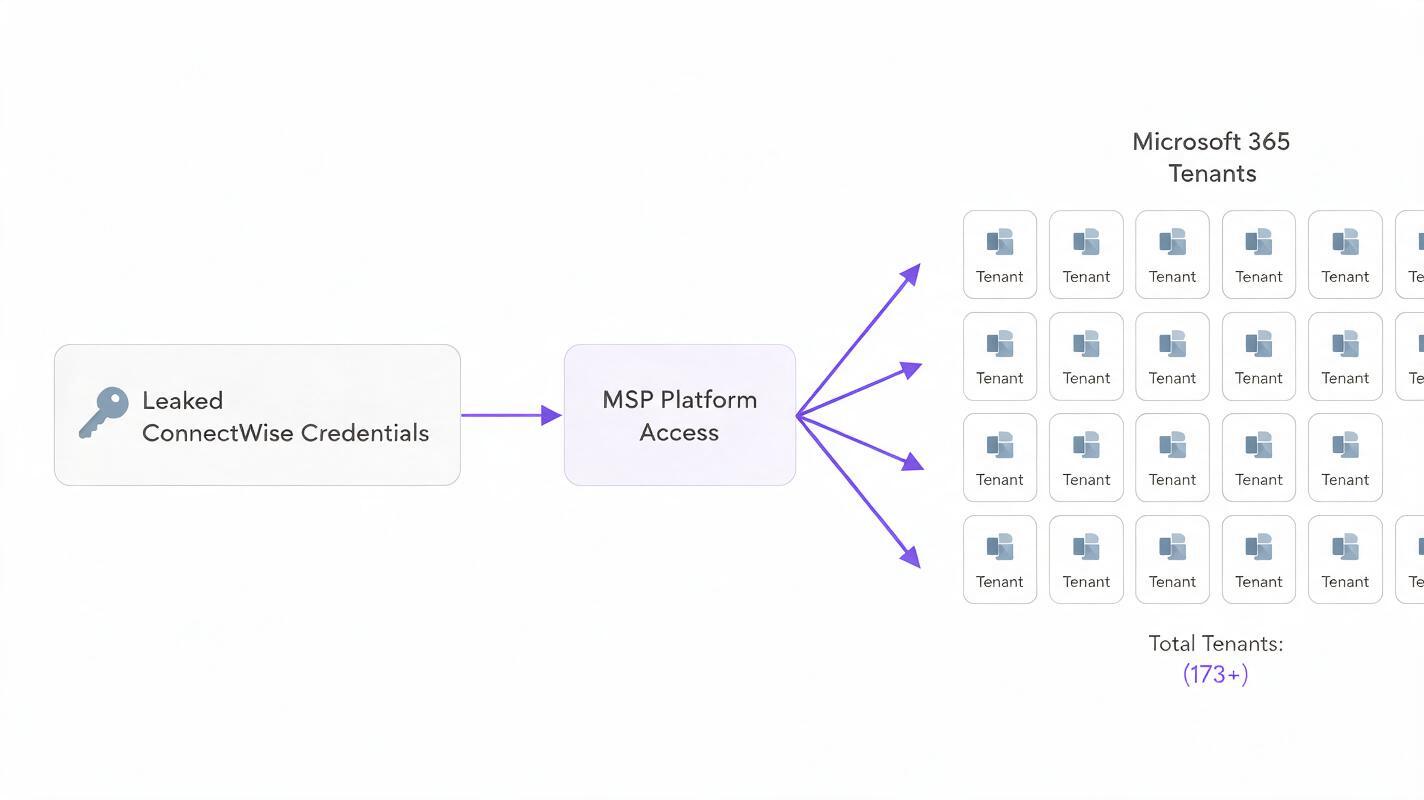
First reported on October 17, 2026 by GreavesNet security news, the ongoing attack leverages stolen ConnectWise credentials to gain unauthorized access to Microsoft 365 environments. The incident is classified as an MSP supply-chain credential abuse event, meaning attackers are using access credentials from a managed service provider platform to target downstream client tenants.
As of the initial disclosure, 173 Microsoft 365 tenants have been confirmed as accessed via the leaked credentials. Security teams advising on the incident have issued two core recommended mitigation actions: immediately rotate all relevant credentials, and enforce multi-factor authentication (MFA) across all privileged and user accounts to block unauthorized access even if passwords are compromised.
ConnectWise is a widely used platform by MSPs to remotely manage client IT infrastructure, monitor systems, and handle support requests. Because MSPs often have broad administrative access to client environments, a single set of compromised credentials can expose dozens or hundreds of client organizations to data theft, service disruption, or further attack.
How MSP Supply-Chain Credential Abuse Puts Organizations at Risk
MSP supply-chain attacks target the trusted access that managed service providers have to their clients' systems, rather than attacking each client individually. When an MSP's platform credentials are leaked or stolen, attackers inherit the same level of access the MSP has to every client environment they manage.
This type of attack is particularly dangerous because it can scale rapidly across hundreds of organizations with a single set of compromised credentials. For many small and medium-sized businesses, including independent creators and small content studios, MSPs handle core IT functions like email management, cloud storage, and software access, making a supply-chain breach difficult to detect or prevent without proactive security measures.
The two core recommended mitigation actions — credential rotation and MFA enforcement — address the root of the risk: stolen passwords alone should not be enough to access sensitive systems. MFA adds a second layer of verification, such as a code from a mobile device or hardware key, that attackers cannot bypass even if they have a user's password.
What This Means for AI Content Creators
For AI content creators and small studios relying on cloud-based tools to produce videos, images, and other digital assets, MSP supply-chain breaches pose a direct threat to workflow continuity and intellectual property security. Many creators use Microsoft 365 for script storage, project collaboration, email communication, and cloud-based file sharing, all of which support their ai video workflow and can be accessed if a tenant is compromised.
A breach could expose unreleased AI video projects, custom prompt libraries, client contracts, and sensitive production data. It could also disrupt access to critical tools, delaying content deadlines and causing lost revenue. For creators who rely on ai automation and integrate their AI workflow with Microsoft 365 or other cloud services managed by an MSP, the risk extends beyond data exposure to potential service outages that halt production entirely.
Creators often manage dozens of separate tool accounts for different AI capabilities, from ai video generator platforms to script writing tools. Each additional account and credential is another potential attack vector, making consolidated security practices even more important for independent creators who may not have dedicated IT support.
Protecting Your AI Production Workflow From Credential Risks
While MSP supply-chain attacks are outside the direct control of most creators, there are proactive measures you can take to reduce your risk and protect your AI content production pipeline:
- Rotate all privileged credentials immediately if you work with an MSP that uses ConnectWise, and confirm your MSP has reset all access credentials on their end.
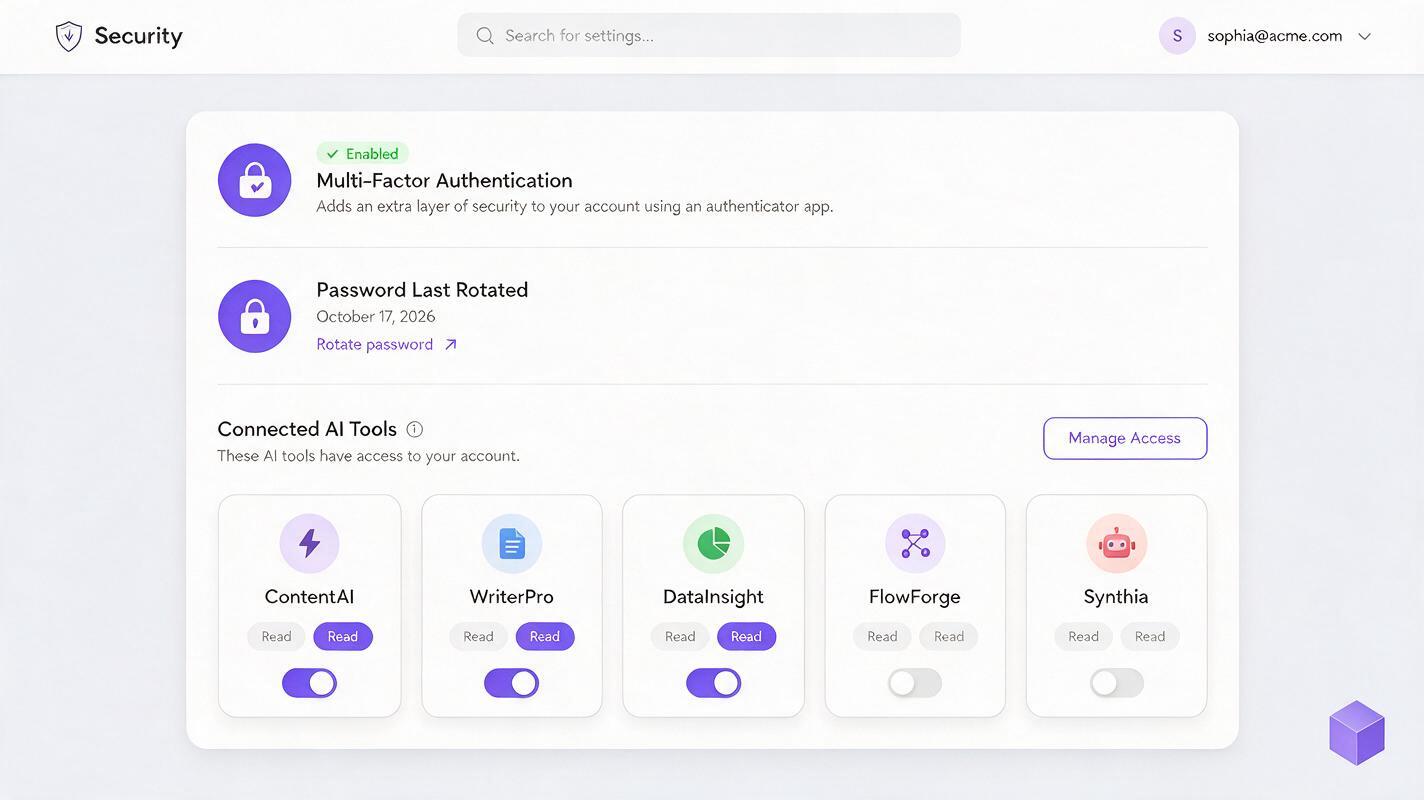
- Enforce multi-factor authentication on every account tied to your production workflow, including email, cloud storage, AI tools, and MSP access portals.
- Review MSP access permissions to ensure your provider only has the minimum level of access needed to support your systems, rather than broad administrative access to all your accounts.
- Monitor for unusual login activity on your Microsoft 365 and other core accounts, and set up alerts for logins from unknown locations or devices.
- Consolidate your AI toolset on a single, secure platform to reduce the number of separate credentials and access points attackers can target.
Consolidating your AI content tools on a platform like MagicBoat reduces your security footprint by letting you access ai image generator, script writing, voiceover, and video editing capabilities all from one secure account. Instead of managing dozens of separate logins for different AI tools, you can handle your entire production pipeline in one place, with centralized account security and access controls.
Key Takeaways
- An active attack using leaked ConnectWise credentials has compromised 173 Microsoft 365 tenants via MSP supply-chain abuse.
- Organizations are advised to rotate relevant credentials immediately and enforce multi-factor authentication across all accounts.
- AI content creators face risks of data exposure and workflow disruption if their MSP or cloud accounts are affected.
- Consolidating AI tools on a single secure platform reduces the number of attack vectors and simplifies security management for creators.
If you're looking to streamline your AI content workflow while reducing credential-related security risks, you can try these models for free on MagicBoat and build your entire production pipeline in one secure, easy-to-use platform.
Keywords
connectwise breach, microsoft 365 security, msp supply chain attack, credential leak, ai workflow security, ai video workflow, cybersecurity for creators